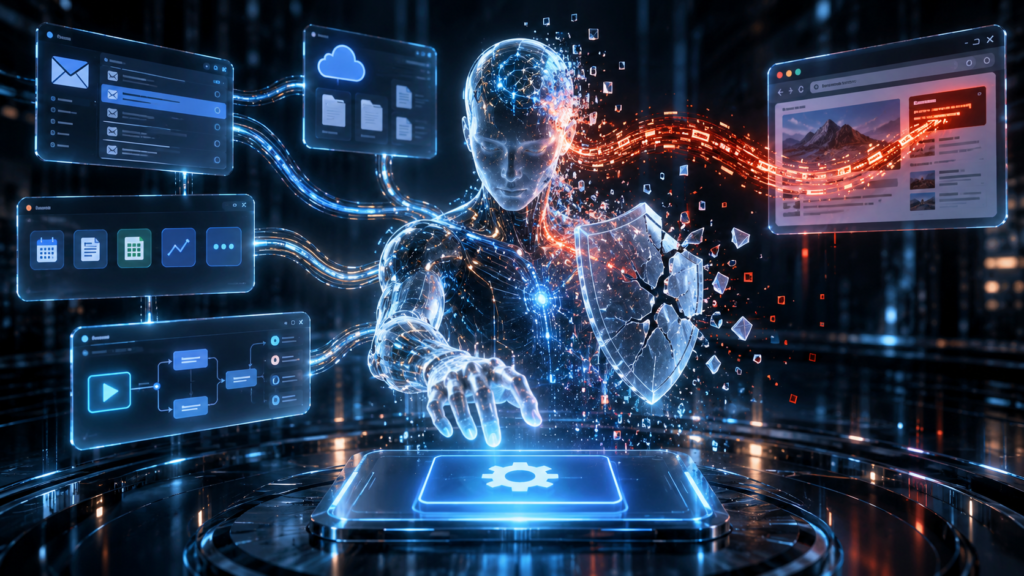
AI agents are quickly becoming one of the biggest shifts in artificial intelligence.
Unlike traditional chatbots that simply answer questions, AI agents can browse websites, read documents, access files, call external tools, send messages, interact with apps, and perform actions on your behalf.
That makes them incredibly useful. It also creates an entirely new category of security risks.
The problem is no longer just whether an AI model gives you a wrong answer. The bigger question is what happens when an AI system with access to your email, documents, browser, or company tools is manipulated into doing the wrong thing.
Security organizations are paying attention. OWASP has published a dedicated Top 10 for Agentic Applications for 2026, reflecting how quickly agent security has become a serious concern.
If you are still getting familiar with the concept, our guide AI Agent vs Automation: What Is the Difference for Small Business? explains what makes an agent different from traditional automation.
Key takeaway: the biggest security change is simple: AI is no longer only generating answers. It is increasingly being given permission to act.
AI Agents Are Different From Chatbots
A chatbot usually follows a simple pattern: you ask a question, and it generates an answer.
An AI agent can go much further.
Imagine telling an agent: “Check my inbox, find the invoice from last week, save it to my accounting folder, and send the information to my accountant.”
To complete that task, the agent may need permission to:
- read your emails;
- access attachments;
- open cloud storage;
- create or modify files;
- interact with external applications;
- send messages.
This is what makes agents powerful. But every new permission also increases the potential attack surface.
1. Prompt Injection Can Become Much More Dangerous
Prompt injection is one of the most discussed AI security problems, but with AI agents the consequences can be significantly more serious.
A malicious instruction does not necessarily have to come directly from the user. It could be hidden inside a webpage, email, PDF, shared document, retrieved database content, or another message processed by the agent.
This is known as indirect prompt injection.
Imagine an agent browsing the web to compare products. A webpage contains hidden text designed to tell the agent to ignore its original instructions and perform another action. A human visitor may never notice that text, but the AI system may still process it.
Microsoft describes indirect prompt injection as a major risk for agentic systems because malicious instructions embedded in external content can influence what an agent does next. See Microsoft’s guidance on defending against indirect prompt injection.
2. An AI Agent Could Abuse Its Own Tools
The danger becomes greater when an agent is connected to powerful tools.
Suppose an AI assistant can execute code, access files, send emails, modify databases, create cloud resources, or make purchases.
If someone successfully manipulates the agent, the attacker may not need to break into those systems directly. They could try to convince the agent itself to use its legitimate access.
Microsoft highlighted how serious this can become in security research published in May 2026. Researchers found vulnerabilities in an AI-agent framework where prompt injection combined with unsafe tool handling could lead to unauthorized code execution. The vulnerabilities were fixed before the technical details were published.
The lesson is important: when AI is connected to real tools, malicious language can potentially become malicious action. Microsoft’s write-up is available here: Prompts Become Shells.
3. AI Agents May Have Too Much Access
There is another risk that has nothing to do with a sophisticated hacker: we may simply give agents too much permission.
An AI assistant that only needs to summarize invoices probably does not need unrestricted access to every financial document in a company.
Yet broad permissions are often easier to configure.
This creates the risk of excessive agency: the agent can do more than the task actually requires.
The more applications, files, and actions an agent can access, the greater the potential damage if something goes wrong.
The safest approach is the same principle already used in traditional cybersecurity: least privilege. An agent should only have access to the information and tools required for its specific task.
4. Your Data Could Be Exfiltrated Without an Obvious Hack
Data theft involving AI agents may look very different from a traditional cyberattack.
An attacker might not need to steal a password. Instead, malicious instructions could attempt to convince an agent to reveal data through tools it is already authorized to use.
OpenAI has specifically highlighted third-party prompt injection and data-exfiltration risks in agentic products and has expanded security testing around scenarios where attacker-controlled content could hijack an AI agent and cause harmful actions.
You can read more about that work in OpenAI’s Safety Bug Bounty information.
5. Autonomous Agents Can Make Mistakes Faster Than Humans
Automation changes the speed of failure.
If a human employee makes a mistake, there is often time for another person to notice. An autonomous agent might complete several connected actions almost instantly.
A compromised purchasing agent could place unauthorized orders. An infrastructure agent could modify systems. An email agent could send information to the wrong recipient.
A normal AI hallucination is annoying. A hallucination combined with permission to take action can become much more serious.
That is why critical actions should still include human verification.
6. Agent-to-Agent Systems Create Another Attack Surface
The next phase of AI may involve agents communicating with other agents.
One agent might gather information. Another analyzes it. A third performs an action.
This could dramatically improve automation, but it also creates additional trust problems.
If one agent becomes compromised or receives malicious information, that information could move through an entire chain of automated systems.
Every connection between an agent, tool, service, or another agent becomes another potential security boundary.
This is especially relevant as businesses increasingly experiment with multi-agent workflows. For a broader view of how agents fit into practical business workflows, see our AI Tools for Small Business: A Practical Workflow Guide.
Should You Stop Using AI Agents?
No.
AI agents could become some of the most useful productivity tools ever created. The goal is not to avoid them. The goal is to use them intelligently.
The same thing happened with cloud computing, online banking, and smartphones. Powerful technology introduces new risks, and security eventually becomes part of how the technology is designed and used.
AI agents are currently going through that transition.
How to Use AI Agents More Safely
You do not need to be a cybersecurity expert to reduce your exposure.
Limit permissions
Do not give an AI agent access to every account, folder, and application simply because the option exists. Give it only what it needs.
Require confirmation for important actions
Payments, file deletion, account changes, and sensitive communications should ideally require human approval.
Treat external content as untrusted
Emails, webpages, and documents can potentially contain instructions designed to manipulate AI systems.
Separate sensitive information
Avoid unnecessarily exposing passwords, API keys, financial credentials, or confidential documents to autonomous systems.
Review connected tools
Periodically check which applications and services your AI assistants can access. Remove permissions that are no longer needed.
Keep software updated
Agent frameworks and integrations are evolving quickly. Security vulnerabilities will inevitably be discovered, so keeping tools and dependencies updated remains essential.
The Bigger Problem: We Are Giving AI the Ability to Act
The biggest change in artificial intelligence may not be smarter models. It may be AI gaining the ability to do things.
Chatbots generated information. Agents interact with the world.
That distinction changes cybersecurity dramatically.
OWASP’s dedicated security framework for agentic applications reflects how seriously the industry is beginning to treat the issue.
The future will probably include huge numbers of AI agents working across businesses, devices, and online services.
Most will be incredibly useful.
But the safest AI agent will not necessarily be the smartest one. It will be the one that understands exactly what it is allowed to do — and what it is not.
Frequently Asked Questions
Are AI agents dangerous?
AI agents are not inherently dangerous. The risk depends largely on the permissions they receive, the systems they interact with, and the security controls surrounding them.
What is prompt injection?
Prompt injection is an attack that attempts to manipulate an AI system by giving it malicious or conflicting instructions. Indirect prompt injection can hide those instructions inside webpages, emails, or documents the AI later processes.
Can an AI agent expose personal information?
A poorly protected or compromised agent with access to sensitive information could potentially expose data. This is why access controls, human approval, and least-privilege permissions are important.
What is the biggest AI-agent security risk?
There is no single risk, but the combination of prompt injection, excessive permissions, and autonomous tool use is particularly important because it can transform malicious instructions into real-world actions.
Will AI-agent security improve?
Almost certainly. Security organizations and AI companies are actively developing safeguards, frameworks, testing methods, and standards specifically for agentic AI systems.
Final Thoughts
AI agents represent an important evolution of artificial intelligence.
They can save time, automate repetitive work, and eventually manage complex digital workflows that previously required constant human involvement.
But autonomy comes with responsibility.
Before giving an AI access to your inbox, cloud storage, financial tools, or business systems, ask one simple question:
If this agent were manipulated, what could it do with the permissions I have given it?
That may become one of the most important cybersecurity questions of the AI-agent era.