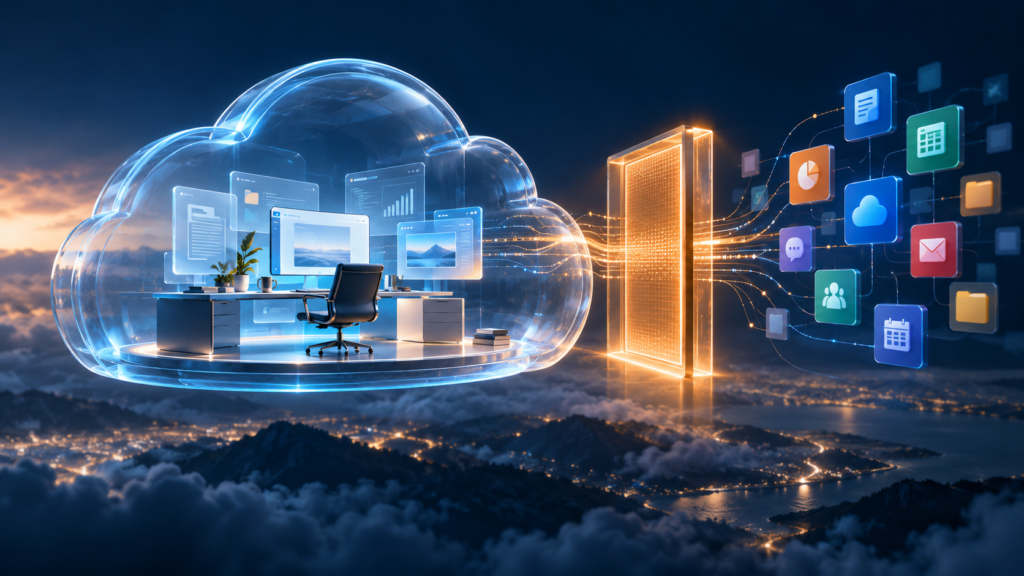
Meta’s Muse is often described as a personal AI agent. The part that makes that claim concrete is the computer Meta gives each user: a dedicated cloud virtual machine with a browser, storage and tools. Here is what Muse Secure VM actually does, and where its safeguards have limits.
What is Muse Secure VM?
According to Meta’s announcement, Muse runs on a dedicated virtual computer in the cloud. Meta’s technical explanation describes it as an isolated Linux virtual machine with a browser, storage, computing resources, and support for tools and concurrent sub-agents.
That setup lets Muse do more than return an answer in a chat window. It can work through a task using a browser and connected services, retain working files and continue certain jobs after the user closes the app. Meta says it returns when a change or approval needs the user’s attention.
A simple example: planning a trip
Suppose you ask Muse to plan a weekend away within a budget. An agent could research options, compare dates and build an itinerary using its browser and any services you have chosen to connect. A booking or payment is a separate step: Meta says Muse asks before sensitive actions such as purchases.
This example explains the promise, but it should not be read as a guarantee that every booking website will work or that the agent will always choose correctly. Results depend on access, site compatibility and the quality of its decisions.
How does Meta separate the agent from sensitive actions?
Muse’s working environment is separated from more sensitive services inside the VM. Meta says the main agent does not directly see real passwords, payment details or service tokens. Connector code and credential storage sit behind separate controls.
A system called Sentinel decides whether connector actions and outbound network requests can proceed. Muse proposes an action; Sentinel checks the user’s permissions and can allow it, deny it or ask the user. Meta also says people can choose which apps to connect and, where supported, grant read access without granting permission to write or send.
For purchases and sending email, Meta describes a user approval step. This matters because instructions found on a web page or in a message may be untrustworthy. Meta’s own security write-up discusses prompt injection and the need for layered protections; it does not claim that errors are impossible.
Why persistence changes the experience
A chatbot typically answers the question in front of it. Muse is designed to retain context, work across connected apps and return to a task later. Meta says it can remember useful preferences and that users can control access or disconnect services.
For a practical AI user, the key question is therefore not only “How good is the model?” It is also “What can this agent access, what can it do without asking, and how can I review its actions?” Meta says Muse provides an audit trail, while its security architecture tries to enforce those permissions outside the agent’s own reasoning.
What should you check before connecting your accounts?
- Start with a narrow permission, such as read-only access where it is available.
- Review each request for access to email, files, shopping or other personal services.
- Check the proposed recipient, merchant, total and details before approving a sensitive action.
- Use the available controls to revoke access you no longer need.
Muse Secure VM is an architecture for giving an AI agent a working computer while placing controls around its actions. It is a meaningful step beyond a simple chat interface, but its real value will depend on reliability and the clarity of those controls in day-to-day use. Small-business readers can also compare that approach with OpenAI in our OpenAI Dots vs Meta Muse comparison.
For the consumer-facing device angle, read our Muse Charm explainer. For the payment side, see our guide to Muse and Stripe Link shopping.
Related Meta Muse coverage
- Why Meta is testing humans behind Muse calls
- The broader Meta Muse strategy
- OpenAI Dots vs Meta Muse for small business